Disclaimer: This blog post reflects the author's opinions regarding industry trends and strategic technology directions. It is provided for informational purposes only and does not modify, amend, or supplement any software licenses, product roadmaps, service level agreements (SLAs), or warranties.
Frontier AI is both exciting and scary. Because it amplifies the power and productivity of digital creators and cyber criminals.
Although mainframes traditionally enjoyed enhanced security through obscurity, innate complexity, and superior reliability, that is no longer a given in the age of AI. In fact, recently released frontier AI models possess deep knowledge of mainframe architecture, allowing attackers to rapidly identify weaknesses and exploit vulnerabilities.
And they’re doing it faster since AI serves as a powerful force multiplier for offensive hackers. This creates an uneven dynamic in a world where defenders must be right 100% of the time, while attackers only need to succeed once.
Because of this, leading organizations must abandon the assumption that mainframes are inherently secure. They must actively and regularly audit their configurations, software, and architecture using best practices, such as penetration tests, and continuously update their security controls with increasing agility. Think monthly, weekly, if not daily, security patches (depending on your security profile, your organization's risk profile, and operational requirements) like every other front-facing piece of software does today.
Rather than treating mainframe security as an occasional cleanup exercise, in the AI era with an exponential increase in attack surfaces, mainframe security and integrity must become a regular, continuous, and risk-driven discipline. That's the central idea behind Broadcom’s intensive AI response.
To stay ahead of malicious actors, Broadcom embeds frontier AI vulnerability-discovery capabilities into our software engineering and security lifecycles. We aim to accelerate vulnerability discovery and deliver verified security fixes faster to safeguard your core enterprise infrastructure without compromising operational stability.
In truth, our advice isn't particularly flashy. And that's precisely why it's worth paying attention to. If knowing is half the battle, here are four things you should know to better protect your organization:
1. Accept that mainframe security is not an occasional cleanup exercise
Keep your software current. Know what you're missing. Prioritize the risky stuff. Automate what you can. Simple, right? In practice, not always.
Mainframe environments can be sprawling, and software versions can accumulate. Dependencies multiply, and maintenance gets deferred. People change jobs. Processes that once made perfect sense become tribal knowledge known by approximately three people — and two of them are thinking about retirement.
Meanwhile, security vulnerabilities aren't waiting around. Because of this, Broadcom recommends a proactive approach to high-impact pervasive (HIPER) fixes, security and integrity (SECINT) fixes, and preventive maintenance rather than treating security updates as an emergency response exercise.
2. Identify, prioritize, and increase your patch frequency
The first step to modern mainframe security is knowing what you actually have and more importantly, what you don’t.
The good news is there are several ways to identify critical fixes, including the SMP/E's ERRSYSMOD report, the z/OSMF Software Management API, the z/OSMF Software Toolkit Plugin, and SYSVIEW Software Risk Assessment. This may sound like ordinary IT housekeeping. But there's an important distinction. You can't manage risks you cannot see.
Once missing fixes are identified, the next question becomes: How urgent are they? Not every vulnerability carries the same risk. Broadcom's SECINT metadata can include common vulnerability scoring system (CVSS) scores, CVSS vectors, and applicable common vulnerabilities and exposures (CVEs), giving organizations information they can use to evaluate risk according to their own policies. That's a much better approach than treating every patch like a fire alarm.
And then there's automation. The z/OSMF Software Management API can identify missing critical updates in JSON format. Broadcom also provides SECINT metadata in CSV and JSON formats, designed to make it easier for organizations to incorporate security information into automated workflows.
That's important because the future of security probably isn't another dashboard somebody promises to check every Friday. It's fewer things that humans have to remember to check.
3. Stay on supported software
There's another piece of the puzzle: software currency. Broadcom recommends knowing the lifecycle of the software you're running, including general availability and end-of-service dates, and staying on supported releases.
It’s like changing the oil in your car. You do it because discovering you needed maintenance after the engine seizes is a lousy strategy. Mainframe security works much the same way. The best time to discover a missing critical fix isn't after something goes wrong. It's when you still have the luxury of planning for it.
We get it—mainframe security can be overwhelming. But there are resources available to help, including Broadcom’s Expert Change Planning, which is designed to help keep you up to date on current severities and establishes a maintenance cadence that matches the risk of the environment.
None of this means the mainframe needs to become something it isn't. It doesn't need to look like the latest cloud platform. It doesn't need a trendy new name. And it certainly doesn't need another "mainframe modernization" PowerPoint explaining why everything you've been doing is suddenly wrong. It just needs continuous updates.
4. Buy into “good maintenance is boring”
The mainframe's greatest strength has always been its reliability. So, the smartest thing we can do is make sure our security practices are just as dependable, especially in the AI era where attacks and exposure are greater than ever.
More than anything, though, the mainframe industry must move away from the "watch when necessary” mindset to “continuously understand, prioritize, and patch increasing risks.” And today that means treating mainframe security not as boring housekeeping, but as an essential part of keeping the world's most dependable computer… dependable.
Learn more about Broadcom Mainframe Software’s security updates.
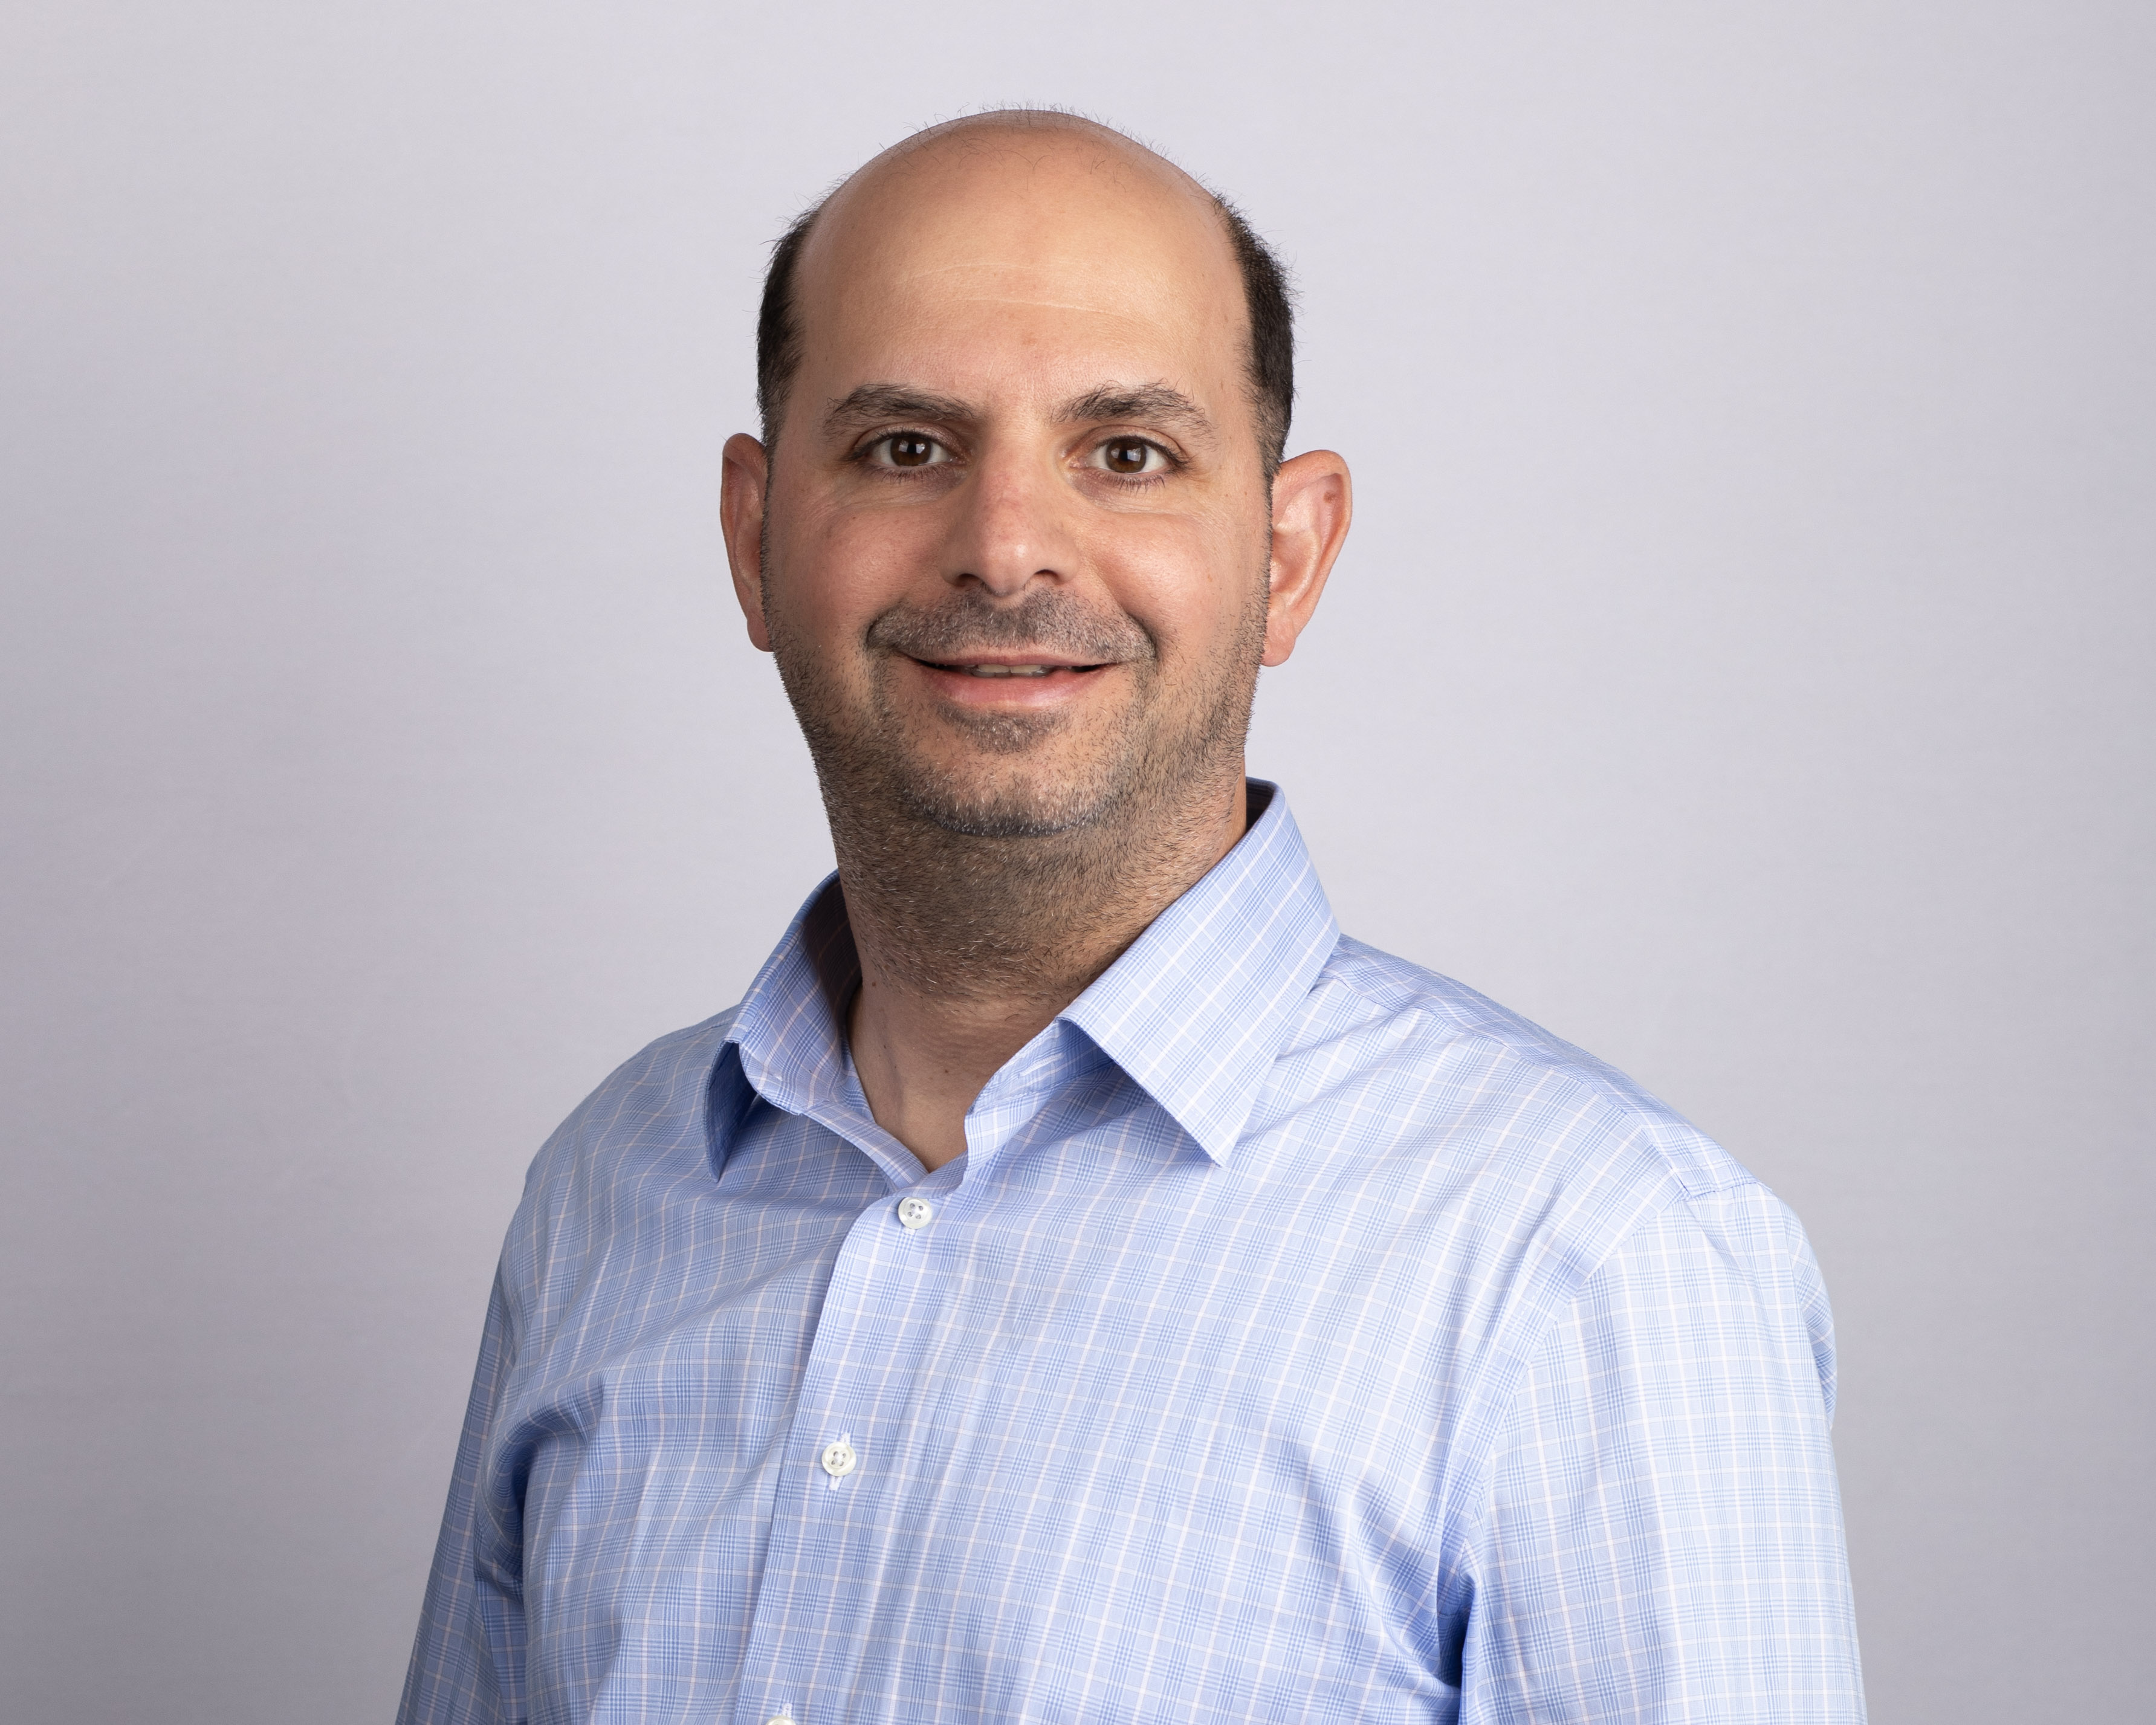 Emre Tunar is the head of mainframe infrastructure engineering & application security for mainframe software solutions at Broadcom, where he leads the strategy and execution of secure software development practices across the company’s mainframe software portfolio. Since April 2026, Emre has been leading Broadcom's Frontier AI driven vulnerability discovery and mitigation program. With over 25 years at Broadcom, Emre brings deep expertise in enterprise software, mainframe modernization, mainframe security, and application security. Throughout his career, Emre has spearheaded the development of next-generation mainframe common services and played a pivotal role in expanding Broadcom’s mainframe security offerings. Emre established the secure software development program and the security champions initiative within the mainframe software division, driving a strong culture of security in the organization. An accomplished engineer, Emre is also the holder of a U.S. patent for a system and method for a common storage object model.